06.
Slider-plugin webshell forensics
Slider-plugin vulnerability leading to webshell; confirmed and traced via security-monitoring logs.
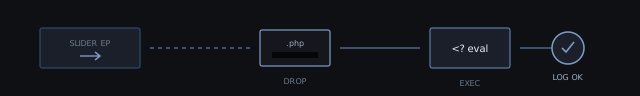
Problem
A WordPress site flagged high-severity outbound PHP activity and intermittent defacement. The installed slider plugin version matched a known unrestricted-upload / RCE class vulnerability. Suspected drop path: wp-content/uploads/… on vhost [REDACTED_HOST].
Detection
Security-monitoring logs (WAF + file-integrity + PHP audit) correlated a crafted multipart upload to the slider endpoint with subsequent execution of a one-liner webshell. Source IP example 10.0.0.77; payload wrote under a randomized media subdirectory, then issued eval-style callbacks.
Action
Took the vhost read-only for uploads, quarantined the webshell and sibling drops, forced plugin update / replacement, rotated application and database credentials, and rebuilt the compromised media tree from clean backups. Added WAF rules for the vulnerable slider routes until all peers were patched.
Result
Webshell lineage confirmed end-to-end with timestamps suitable for customer IR reporting. No evidence of deeper host compromise beyond the web root. Detection signatures promoted to the shared WordPress attack detector ruleset.